Result description
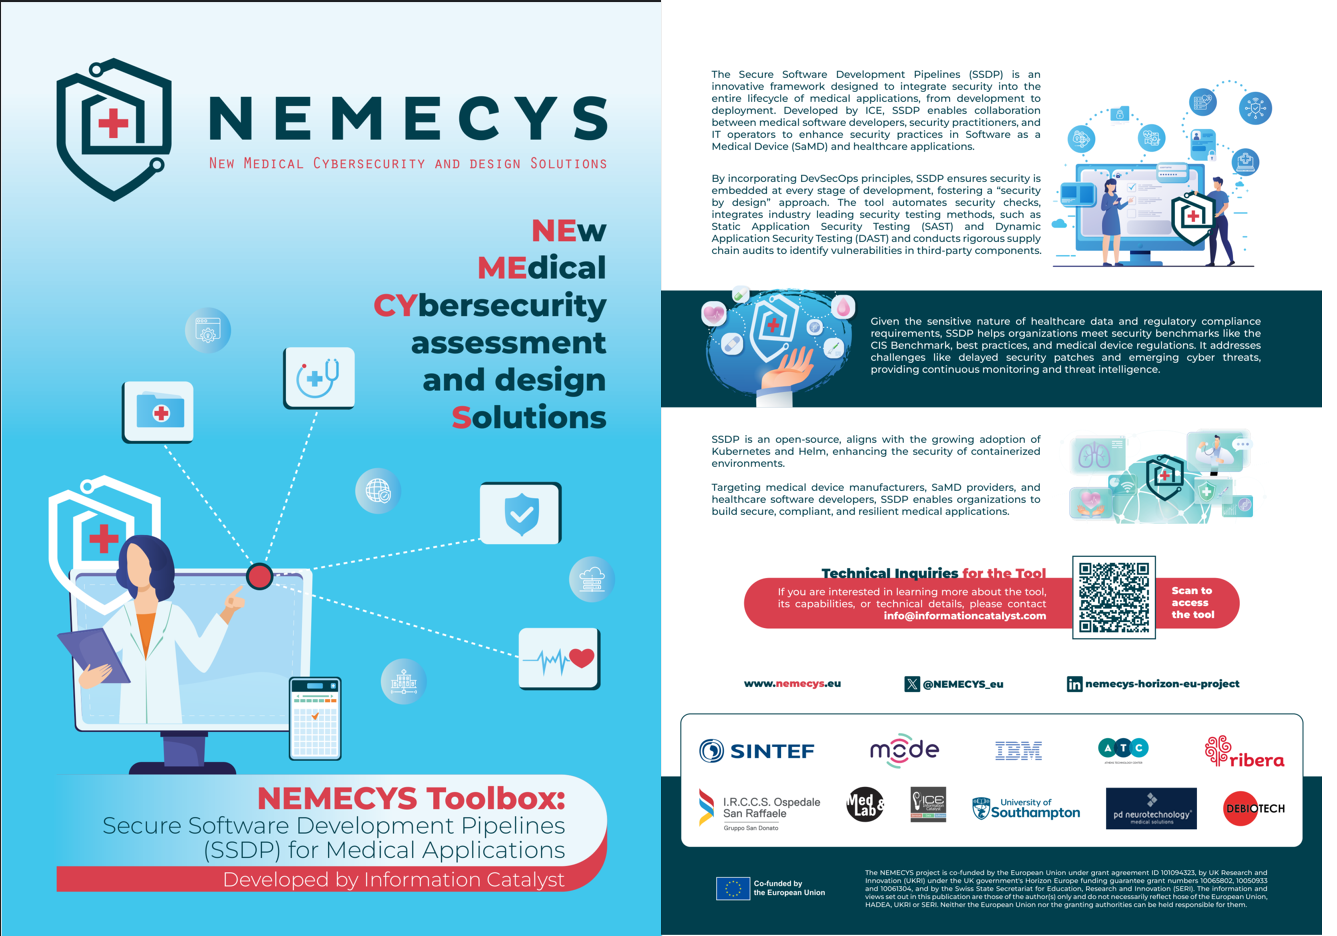
The Secure Software Development Pipelines (SSDP) for Medical Applications is an integrated DevSecOps solution designed to embed cybersecurity controls throughout the entire lifecycle of Software as a Medical Device (SaMD) and healthcare applications.
SSDP automates security validation across Continuous Integration and Continuous Deployment (CI/CD) environments, incorporating static and dynamic application security testing (SAST/DAST), software composition analysis, supply chain verification, container security, infrastructure-as-code validation, and continuous monitoring.
The framework enables:
- Security-by-design implementation
- Early vulnerability detection and remediation
- Traceability and compliance support
- Secure containerised and cloud-native deployments
- Risk-based security validation across CI, QA, security, performance, staging, and production environments
SSDP strengthens digital resilience in medical software ecosystems and reduces systemic cyber risks affecting healthcare infrastructures.
Addressing target audiences and expressing needs
- Business partners – SMEs, Entrepreneurs, Large Corporations
- Technology Transfer Expertise
- Expanding to more markets /finding new customers
-Industrial partners (SMEs and large enterprises) to pilot and validate the solution in operational environments
-Technology transfer and commercialisation partners to support go-to-market strategy and IP exploitation
-Cybersecurity and DevOps solution providers interested in integration or joint offerings
-Public or private investors to support scaling and productization.
-Research collaborations to further enhance automation, AI-assisted security testing, and compliance verification
- Public or private funding institutions
- Other Actors who can help us fulfil our market potential
- Research and Technology Organisations
R&D, Technology and Innovation aspects
SSDP has been demonstrated in operational medical software environments, integrating automated security controls across CI/CD pipelines with a Greek MD Manufacturer.
Next steps include industrial pilots with medical software providers, productisation as a modular security solution, regulatory alignment support, and scaling through partnerships with investors and healthcare technology integrators.
SSDP is built as a modular, cloud-native framework that integrates with existing CI/CD and Kubernetes environments. Its automation-first design reduces operational overhead and enables rapid onboarding of new clients. The open-core model with paid support and services allows revenue growth without proportional cost increases, ensuring scalable and sustainable expansion.
SSDP can be replicated across medical device manufacturers, SaMD providers, and regulated software organisations adopting cloud-native infrastructures. Its modular architecture and standards-based approach enable deployment in different regulatory and operational contexts, promoting secure-by-design practices and long-term digital resilience across healthcare ecosystems.
SSDP promotes long-term digital resilience by embedding security and compliance throughout the software lifecycle. Its automation-driven approach reduces vulnerability exposure, supports evolving regulatory requirements, and strengthens healthcare cybersecurity. The recurring service model and modular design ensure continuous improvement and sustainable market viability.
- Europe
- United Kingdom